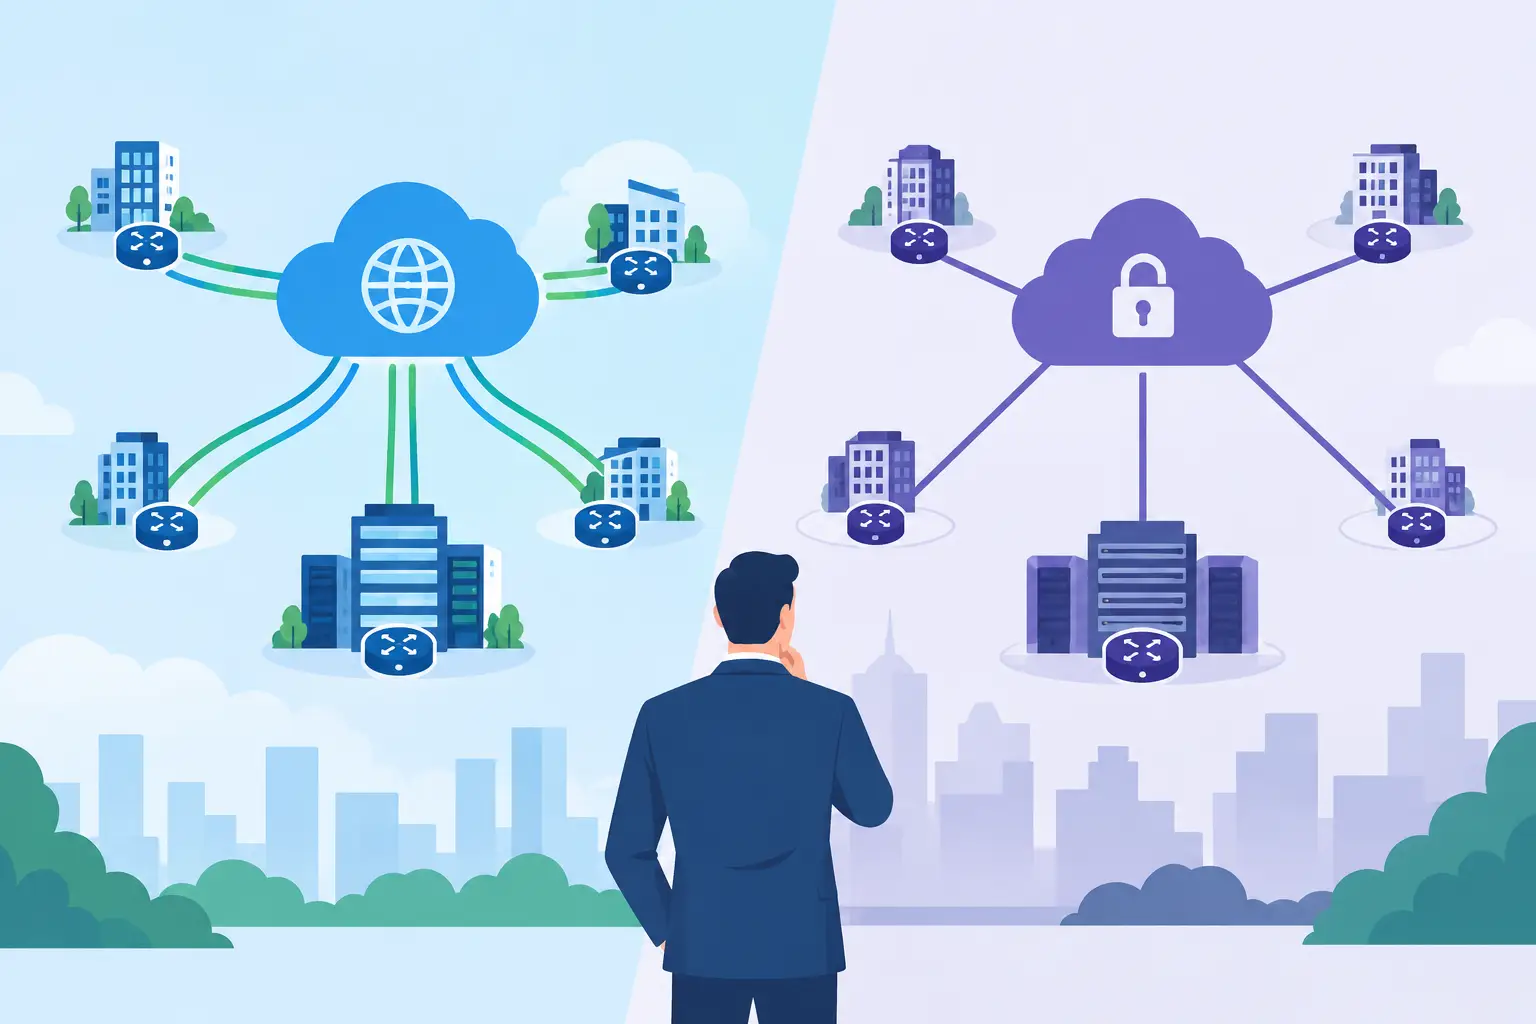
A branch losing connectivity is not just an IT inconvenience. Card terminals stop processing, cloud applications become slow, staff resort to personal hotspots, and customers notice. The real question in the SD-WAN vs MPLS networks discussion is not which technology has the better acronym. It is which approach keeps each site productive when broadband performance changes, a circuit fails, or demand rises.
For multi-site businesses, the answer is rarely about buying a single connection. It is about building a wide area network that supports the applications, security controls and people your operation depends on – without creating another collection of providers to manage when something goes wrong.
What MPLS does well
MPLS, or Multiprotocol Label Switching, is a private carrier network designed to connect sites through managed paths. Rather than sending business traffic across the public internet, an MPLS provider carries it within its own network and can apply defined classes of service for different types of traffic.
That predictability has made MPLS a long-standing choice for organisations with critical voice, transaction or line-of-business applications. A retailer may prioritise payment traffic. A professional services firm may prioritise voice calls between offices. Where the network provider can offer committed bandwidth, controlled routing and performance commitments, MPLS can provide a stable foundation.
MPLS is also straightforward in principle. Each location joins the same managed private network, and traffic between sites follows an established route. For businesses with a small number of permanent sites, known traffic patterns and limited need for direct cloud access, that simplicity can be valuable.
However, private does not automatically mean secure. MPLS separates traffic from the public internet, but it does not replace firewalls, access controls, endpoint protection, monitoring or backup. It is one part of a security design, not the whole design.
How SD-WAN changes the picture
Software-defined wide area networking, or SD-WAN, uses software and centrally managed policies to direct traffic across one or more connection types. These may include fibre broadband, fixed wireless, 4G or 5G, and in some cases an MPLS circuit.
Instead of treating every application identically, SD-WAN identifies traffic and applies rules. A video meeting can be sent over the connection currently delivering the best real-time performance, while less time-sensitive traffic uses another path. If a primary circuit fails, the service can move traffic to an available backup connection without waiting for someone at the site to intervene.
This is particularly useful when a business relies heavily on cloud platforms. Many applications now live outside the head office or data centre: Microsoft 365, cloud point-of-sale platforms, hosted phone systems, security services and line-of-business software. Backhauling all that traffic through a central location can add delay and create an unnecessary dependency. SD-WAN can provide controlled local internet breakout, allowing approved traffic to reach cloud services more directly.
The operational advantage is visibility. A well-managed SD-WAN service should show which connections are available, how applications are performing and where faults are occurring. That gives support teams a clearer starting point than asking a site to reboot equipment and hope for the best.
SD-WAN vs MPLS networks: the practical differences
The most meaningful differences sit around performance, resilience, cost and management.
MPLS generally offers more predictable performance because the carrier controls the underlying private network. This can suit applications that need consistent latency and carefully managed quality of service. But a single MPLS circuit at a site can still become a single point of failure unless there is a diverse secondary connection.
We've got your back
SD-WAN does not make an unreliable connection reliable by itself. Its strength is using multiple available paths intelligently. A branch with fibre and 5G backup may keep operating through a fibre outage, even if non-essential traffic is temporarily reduced. For many operationally busy businesses, continued trading at a reduced level is far better than a full outage.
Cost structures also differ. MPLS has traditionally carried a higher price where dedicated access, managed capacity and carrier commitments are required. SD-WAN can make better use of business-grade internet services and lower-cost backup options. That can reduce WAN spend, especially across many locations, but the comparison must include the cost of the SD-WAN platform, managed routers, security, monitoring and support.
Neither option should be chosen purely on monthly circuit price. A cheaper connection that leaves a site offline during the busiest trading period can cost far more than it saves. Equally, paying for premium MPLS at every small site may be difficult to justify when cloud applications and a properly designed broadband-plus-mobile setup would meet the real requirement.
Security needs to follow the traffic
The move towards internet-based connectivity changes where security controls need to sit. If branch traffic goes directly to cloud services, protection cannot rely only on a firewall at head office. Each site needs policies that are appropriate to its users, devices and applications.
For SD-WAN, this often means encrypted tunnels between locations, next-generation firewall capability, web filtering, intrusion prevention and central policy management. The exact design depends on the environment. A site processing card payments has different segmentation and compliance needs from a small office with a handful of managed laptops.
MPLS environments need the same discipline. Private connectivity can reduce exposure, but ransomware, compromised credentials, insecure devices and poorly configured remote access do not disappear because the WAN is private. Security should be monitored continuously, with clear ownership for alerts, patching and escalation.
This is where fragmented supplier arrangements create risk. If one provider supplies connectivity, another manages the firewall, a third owns Wi-Fi and a fourth supports payment devices, fault resolution can become an exercise in passing responsibility. A single partner that can see the network and the security controls can isolate problems faster and take ownership of the outcome.
Which model fits your business?
MPLS may still be the right choice when you have a requirement for tightly controlled, consistent connectivity between fixed sites, particularly where legacy applications remain central to operations. It can also be appropriate where a provider can deliver the service levels and geographical reach your business needs.
SD-WAN is often the stronger fit for organisations that use cloud applications, have a mix of connection types, need fast failover, or want more flexibility as sites open, relocate or change size. It is especially compelling for retailers, hospitality groups and service businesses that cannot afford a branch to lose access to payments, phones or cloud systems.
There is also a third option: use both. A hybrid WAN can retain MPLS for locations or applications that benefit from predictable private connectivity, while SD-WAN uses broadband and mobile services for resilience, cloud access and lower-priority traffic. This can be a sensible transition path rather than a disruptive replacement programme.
The right design starts with how the business actually works. Review the applications used at every site, the impact of an outage, peak trading periods, available connection types, security obligations and the support model. Do not assume all branches need the same service. A busy flagship location may warrant diverse primary circuits, while a low-traffic office may be well served by fibre with managed 5G failover.
Make support part of the network decision
A WAN design is only as useful as the support behind it. Ask who monitors each connection around the clock, who identifies whether a fault sits with the circuit, router, Wi-Fi or firewall, and who coordinates the fix. Also ask what happens when a site loses its primary path at 8pm on a Saturday.
Vetta Group approaches this as an operational service rather than a box-and-circuit sale. Connectivity, managed IT and security work best when they are designed together, monitored continuously and supported by people who can see the full picture.
Choose the network model that gives your teams the confidence to keep serving customers, even when the unexpected happens. That is the measure that matters long after the installation is complete.